Nigeria Managed SOC Market 2026: How Cybersecurity Regulation Is Reshaping Enterprise Security Spending
Nigeria’s Cybersecurity Rules Are Turning Managed SOC Into Strategic Infrastructure
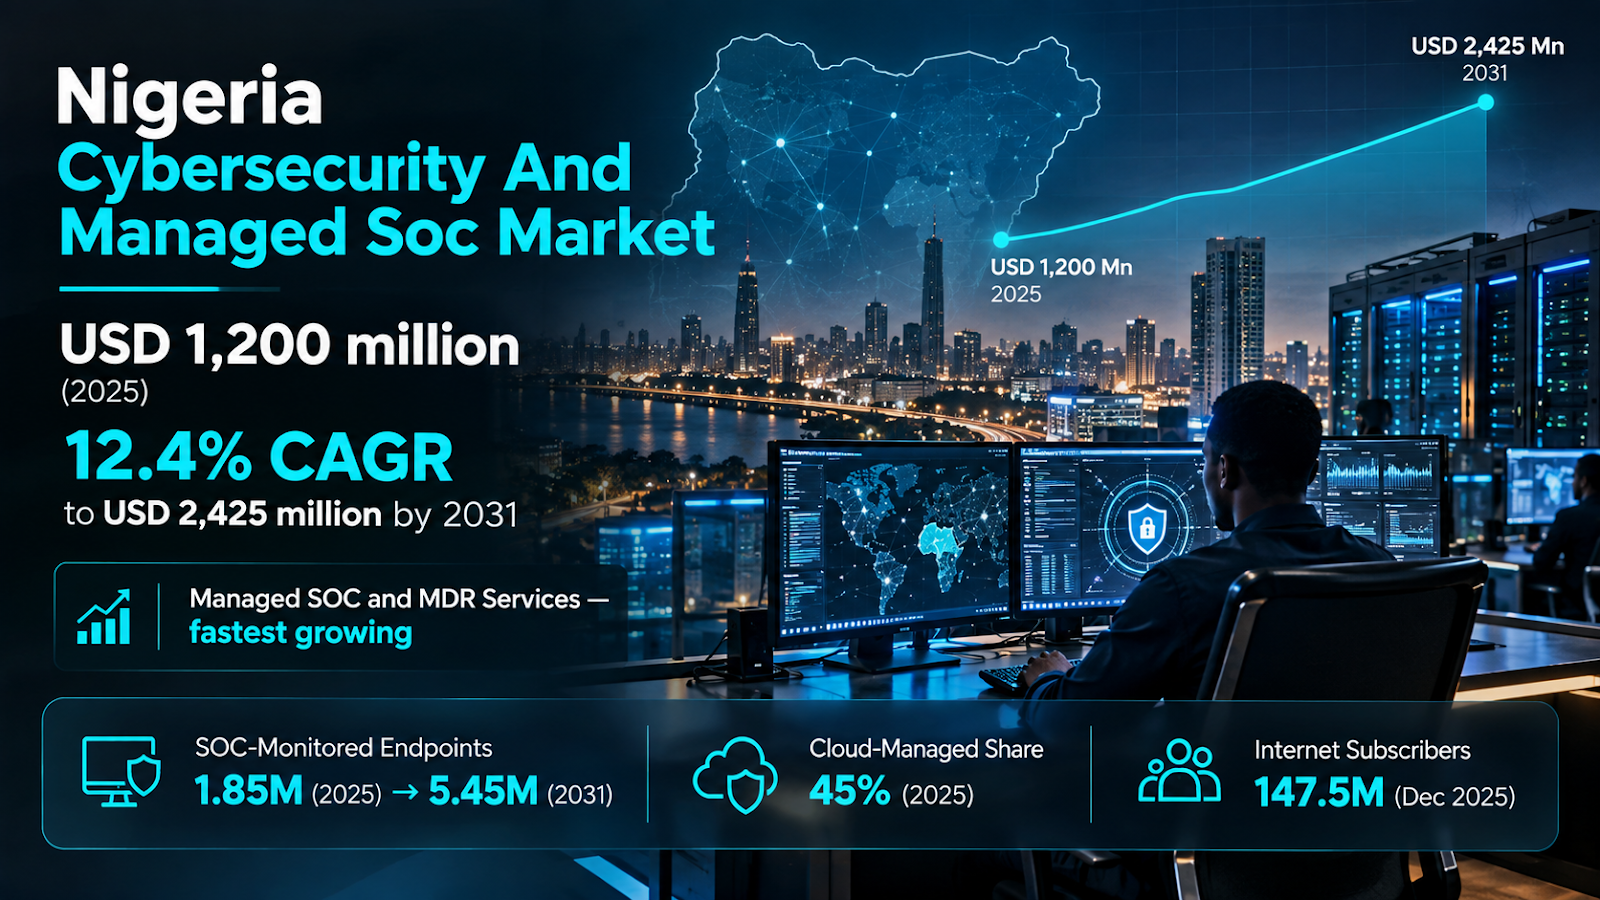
Nigeria’s cybersecurity market is entering a phase in which regulation is becoming as important a demand driver as the threat environment itself. For executives evaluating digital risk, the central question is shifting from whether to invest in cybersecurity to how quickly security operations can be converted into a continuously monitored, auditable and regulator-ready capability. Analysis from Ken Research places the Nigeria Cybersecurity and Managed SOC Market at USD 1,200 million in 2025, with revenue projected to reach USD 2,425 million by 2031 at a 12.4% CAGR. Managed SOC and MDR services are among the areas positioned to benefit as compliance and operational complexity converge.
Policy Shift: Cybersecurity Is Moving From Best Practice to Demonstrable Compliance
The regulatory catalyst is becoming increasingly concrete. Nigeria’s Data Protection Commission issued the General Application and Implementation Directive 2025 on 20 March 2025, strengthening the operational framework surrounding the Nigeria Data Protection Act. The Commission states that applicable controllers must submit annual Compliance Audit Returns before 31 March, while a Data Controller or Processor of Major Importance can face a remedial fee up to the greater of NGN 10 million or 2% of annual gross revenue from the preceding financial year.
Critical infrastructure obligations are expanding simultaneously. The federal Critical National Information Infrastructure Order formally establishes a framework for identifying and protecting designated ICT systems, networks and infrastructure whose disruption could affect economic activity, national security, public health or government operations. The Order also envisages minimum standards, rules and procedures for protecting designated CNII.
- Boards should therefore interpret data-protection and CNII obligations as operational-security requirements rather than legal-documentation exercises, because demonstrating accountability increasingly requires evidence that risks are continuously identified, monitored, escalated and remediated.
- Security leaders should map every regulatory obligation to an auditable control, named owner, telemetry source and response workflow so that compliance reporting becomes an output of day-to-day security operations rather than a disruptive annual project.
Market Impact: Regulation Is Increasing the Value of Continuous Monitoring
The policy shift intersects with a rapidly expanding digital attack surface. NCC statistics show 147,519,262 GSM internet subscriptions and 112,665,176 broadband subscriptions in December 2025. More connected customers, cloud applications and transaction endpoints create more telemetry to inspect and more identities to defend.
Threat pressure reinforces the argument. On 30 April 2026, ngCERT reported a significant rise in high-impact incidents affecting Nigerian organisations, citing phishing, ransomware, business email compromise and data breaches, with particular concern for Critical National Information Infrastructure. A separate August 2026 advisory warned that business email compromise increasingly includes credential harvesting, smishing, vishing and AI-assisted impersonation.
This environment supports recurring security economics. Ken Research models 1.85 million SOC-monitored endpoints, approximately 2,300 active managed-security clients and a 45% cloud-managed share in 2025. Monitored endpoints are projected to reach approximately 5.45 million by 2031, meaning telemetry volumes can scale substantially faster than traditional analyst-heavy operating models.
The adjacent Nigeria cybersecurity managed services market and cloud protection market reinforce the same direction: enterprises are shifting toward outsourced detection, incident response, compliance monitoring and cloud-oriented security as environments become harder to supervise internally.
Strategic Action: Build Compliance Into the Security Operating Model
Early movers can create an asymmetric advantage by treating regulatory readiness as an architecture decision. The objective should not be to accumulate disconnected security tools, but to build evidence-generating security operations capable of demonstrating governance, detection, escalation, containment and recovery.
Don’t miss the next turning managed SOC into strategic infrastructure shift. Ken Research continuously publishes new market intelligence, forecasts and industry analysis. Add Ken Research as a Preferred Source on Google to discover more of our research when your next market question comes up.
- Enterprises should prioritize managed SOC or MDR contracts with measurable response SLAs, documented escalation paths, identity monitoring and regulator-ready reporting, particularly where internal analyst capacity cannot provide reliable 24-hour coverage.
- Cloud and hybrid environments should be consolidated into common telemetry and incident-management workflows so that organisations can demonstrate consistent controls across endpoints, identities, applications and infrastructure instead of maintaining fragmented compliance evidence.
- Financial institutions should align investments with the CBN’s risk-based cybersecurity approach, which addresses governance, cyber-risk management, resilience, monitoring, reporting and regulatory compliance, while using sector intelligence such as the Nigeria cybersecurity in financial services market to benchmark evolving demand.
The Regulatory Catalyst Is Reshaping the Buying Decision
Nigeria’s policy direction creates a clear relationship between government action and market outcomes: stronger data-protection accountability, CNII protection requirements and sector-specific cybersecurity governance increase the need for demonstrable, continuous security controls; that requirement, in turn, strengthens demand for managed monitoring, MDR, cloud security, identity analytics and incident-response retainers.
The strategic advantage belongs to organisations that operationalise these requirements before audits, incidents or procurement deadlines force action. Managed SOC should therefore be evaluated not simply as outsourced IT security, but as part of the enterprise compliance, resilience and risk-governance infrastructure.


Comments
Post a Comment